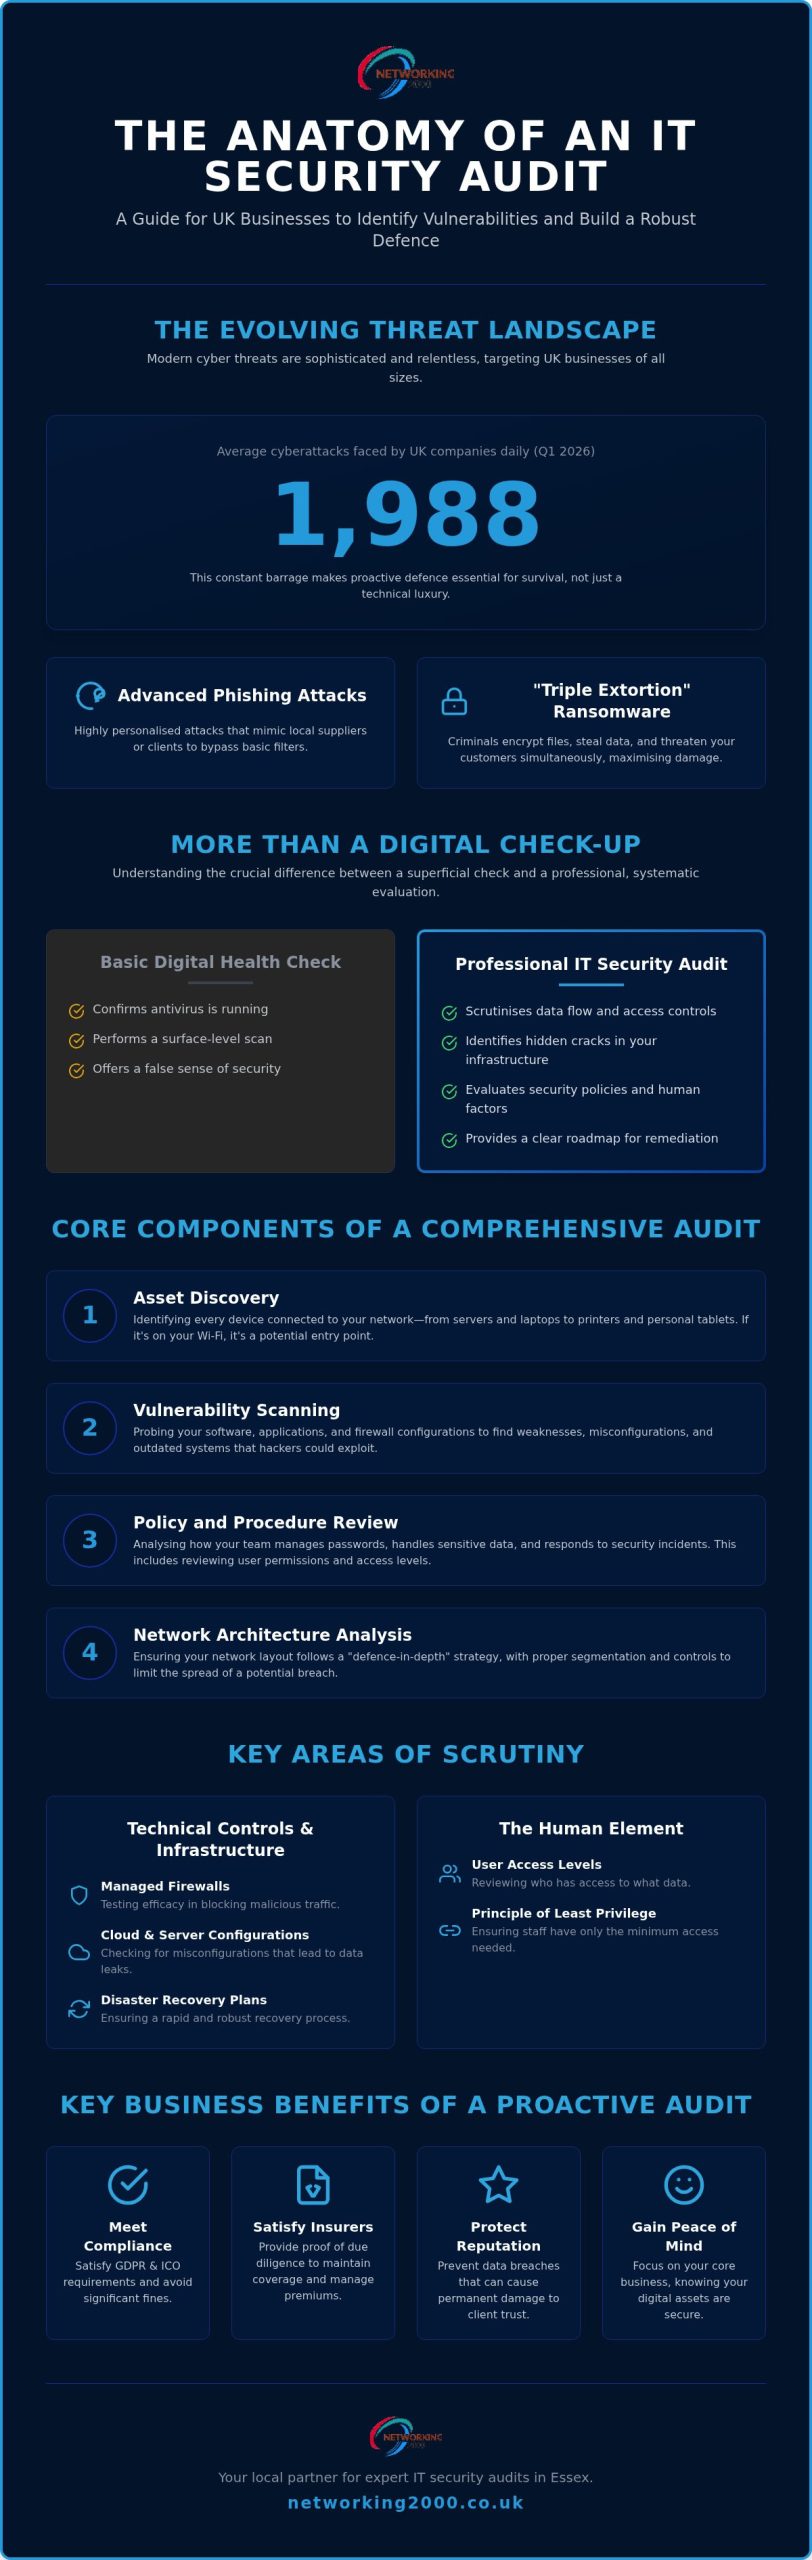
Did you know that UK companies faced an average of 1,988 cyberattacks every single day during the first quarter of 2026? It is a staggering statistic that makes the fear of a data breach feel very real, especially when you’re already struggling with complex insurance requirements and confusing technical jargon. You need to protect your hard-earned reputation, but you don’t want to get lost in a sea of “cyber-speak” or unnecessary complexity.
We understand that pressure. At Networking2000, we believe that staying secure shouldn’t be a constant headache. Booking a professional IT security audit Essex is the most practical way to clear the fog and find exactly where your business is vulnerable. This guide will show you how a thorough assessment identifies hidden risks, ensures you meet the latest UK data protection standards, and builds a robust defence around your operations. We’ll explore the real-world benefits of proactive testing and explain how a clear security roadmap allows you to focus on your core work with total peace of mind.
Key Takeaways
- Learn why a professional assessment is far more effective than a basic digital health check for identifying real-world vulnerabilities.
- Discover the essential components of a thorough IT security audit Essex, from identifying connected devices to probing firewall configurations.
- Compare the UK government-backed Cyber Essentials scheme with bespoke audits to determine the best fit for your specific business needs.
- Follow practical steps to organise your software licences and critical data, ensuring your business is fully prepared for a successful audit.
- Understand how partnering with a local veteran can help you implement proactive measures like managed firewalls to secure your long-term future.
What is an IT Security Audit and Why Does Your Essex Business Need One?
An IT security audit Essex is far more than a simple digital check-up. It is a systematic, deep-dive evaluation of your firm’s entire digital infrastructure and security policies. Many business owners confuse a standard “health check” with a professional audit. While a health check might confirm your antivirus is running, a full audit scrutinises how data flows through your business, who has access to it, and where the hidden cracks lie. To get a broader perspective on the technical standards involved, you can explore What is an Information Security Audit? to see the rigorous framework we follow.
By 2026, relying on traditional antivirus software is like locking your front door but leaving the windows wide open. Modern cyber threats are sophisticated. They bypass basic filters using AI-driven social engineering. A professional audit identifies these gaps before a criminal does. It also plays a vital role in maintaining GDPR compliance. Under the Data (Use and Access) Act 2025, the Information Commissioner’s Office (ICO) has significant powers to fine businesses that fail to protect personal data. For an Essex-based company, an audit isn’t just about technology; it’s about legal and financial survival.
The Evolving Threat Landscape for Essex SMEs
Local firms in Wickford, Chelmsford, and Southend are increasingly in the crosshairs of cybercriminals. Attackers often target smaller enterprises because they assume defences will be weaker than those of large London corporations. We’ve seen a rise in highly personalised phishing attacks that mimic local suppliers or clients. Ransomware has also evolved into “triple extortion” tactics, where criminals encrypt your files, steal your data, and threaten your customers simultaneously. In a local community, the reputational damage of a breach can be permanent. News travels fast, and losing client trust is often more expensive than the technical recovery itself.
Regulatory and Insurance Requirements
The insurance market has changed. Professional indemnity and cyber insurance providers now frequently demand evidence of regular, professional IT security audits. They want to see that you’re proactive, not just reactive. Achieving certifications like Cyber Essentials or the audited Cyber Essentials Plus has become a baseline requirement for many supply chains and government contracts. An audit provides you with a “defensible position.” If the worst happens, you can prove to regulators and insurers that you took every reasonable step to secure your network. This due diligence is essential for keeping your premiums manageable and your business eligible for high-value contracts.
The Core Components of a Comprehensive IT Security Audit
A professional IT security audit Essex involves more than just running a basic scan. It is a multi-layered process that looks at your hardware, software, and the people who use them. We start with asset discovery. This means identifying every single device connected to your network, from servers and laptops to that old printer in the corner or a staff member’s personal tablet. If it’s on your Wi-Fi, it’s a potential entry point. Vulnerability scanning follows. We probe your software and firewall configurations to find weaknesses that hackers could exploit. We also perform a policy review. This looks at how your team manages passwords and handles sensitive data. Finally, we analyse your network architecture to ensure your layout follows a “defence-in-depth” strategy.
Technical Controls and Infrastructure
We pay close attention to your perimeter defences. This includes testing the efficacy of managed firewalls to ensure they’re blocking malicious traffic effectively. We also look at your cloud storage and local server configurations. Misconfigured cloud settings are a leading cause of data leaks in 2026. A vital part of this technical review is evaluating the robustness of your disaster recovery plan. We ensure that if a breach occurs, your business can get back on its feet quickly. Many of these technical controls are aligned with the Cyber Essentials scheme, which sets a baseline for UK business security.
The Human Element: User Behaviour and Permissions
Technology is only half the battle. We review user access levels to ensure the “principle of least privilege” is in place. This means staff only have access to the specific files they need for their jobs. We also assess staff awareness. Are your employees trained to spot sophisticated phishing tactics? Remote work adds another layer of risk. We evaluate the security measures for staff working outside your Wickford office to ensure their home connections don’t create a backdoor into your business network. Strengthening these areas turns your team into your first line of defence. If you’re ready to secure your infrastructure, our team provides professional IT security services tailored to your needs.
Cyber Essentials vs. Bespoke Security Audits: Which is Right for You?
Choosing the right type of IT security audit Essex depends on your business size, sector, and specific risks. Cyber Essentials is the UK government’s baseline standard. It’s affordable and focuses on five fundamental controls: firewalls, secure configuration, user access control, malware protection, and patch management. While it covers the basics, it doesn’t always account for complex network layouts or specific industry threats. For businesses looking for a truly comprehensive IT security audit, a bespoke approach is often the better path. This deep-dive method scrutinises every corner of your infrastructure. It identifies nuanced gaps that a standardised checklist might overlook, such as specific cloud misconfigurations or hardware end-of-life issues.
The Benefits of Cyber Essentials Certification
Cyber Essentials is more than just a badge. It gives your business a competitive edge when tendering for local government contracts in Essex. Many public sector bodies and larger supply chains now require this certification as a minimum. It also helps with your bottom line. Insurers often reduce premiums when they see verified security standards in place. By implementing the five basic controls, you protect against roughly 80% of common, low-level cyber threats. It’s a quick win for micro and small businesses that need a reliable starting point. It requires less time than a full audit but provides immediate, tangible proof of your commitment to security.
When to Invest in a Deep-Dive Bespoke Audit
Sometimes a standard certification isn’t enough. If your Essex firm handles highly sensitive client data in the finance or legal sectors, you need a more rigorous assessment. Bespoke audits are essential for companies managing a hybrid workforce with multiple remote entry points. These audits evaluate your specific workflow and digital transformation goals. They ensure your security scales alongside your business. A custom audit looks at your unique network architecture and user behaviours. It provides a tailored roadmap that standard schemes simply can’t offer. You get a deeper analysis of your internal policies and physical security, ensuring every “safe pair of hands” in your organisation is actually following best practices. This professional IT security audit Essex ensures your defences are built specifically for the way you work.
How to Organise Your Essex Business for a Successful Audit
Preparing for an IT security audit Essex shouldn’t feel like a chore. Think of it as an opportunity to tidy your digital house. The more organised you are at the start, the more value you’ll get from the final report. We recommend a structured approach to ensure the process is thorough and efficient. By following a clear roadmap, you’ll help our team identify vulnerabilities faster without missing critical details. It’s about being proactive and ensuring your “safe pair of hands” has everything they need to protect you.
- Step 1: Create a comprehensive list of all IT assets and software licences. This includes everything from desktop PCs to mobile phones and tablets.
- Step 2: Map out where your most critical data lives. Is it on a local server in Wickford, or spread across various cloud platforms?
- Step 3: Brief your staff. Cooperation is vital, especially when we review user behaviours or test phishing awareness.
- Step 4: Look back at past incidents. Reviewing previous “near misses” helps us understand where your current defences have already been tested.
- Step 5: Choose a single point of contact. Having one person to handle requests keeps the project on track and prevents communication breakdowns.
Gathering Essential Documentation
Documentation is the backbone of a successful audit. You’ll need to compile a list of every third-party vendor that has network access, such as external accountants or maintenance firms. We’ll also need to see your current password policies and remote access protocols for hybrid workers. If you already use managed IT support services, having a summary of those existing arrangements is incredibly helpful. It allows us to see how your current support system integrates with your security measures. This clarity ensures we don’t duplicate work or overlook managed endpoints.
Minimising Operational Disruption
A common worry for Essex business owners is that an audit will slow down the working day. We work hard to prevent this. We schedule technical scans during off-peak hours to ensure your network performance remains steady. To help us, make sure the audit team has all necessary access permissions and administrator credentials ready in advance. Most importantly, communicate the “why” to your team. When staff understand that the audit is there to protect their work and the company’s reputation, they’re far less likely to feel anxious about the process. If you want to start your journey toward a more secure business, contact our Essex-based IT security experts today for a professional consultation.
Networking2000: Your Local Partner for Expert IT Security Audits
Networking2000 has been a reliable fixture of the Essex business community since 1998. With over 25 years of experience, we’ve seen the digital landscape transform from basic dial-up to the complex, AI-driven environment of 2026. We pride ourselves on being a “safe pair of hands” for local SMEs. When you book an IT security audit Essex with us, you aren’t just getting a technical scan. You’re getting a partnership built on transparency and practical advice. We explicitly avoid dense jargon. Our goal is to provide clear, actionable steps that protect your livelihood without making things unnecessarily complicated.
The Networking2000 Audit Process
Our approach is methodical and designed to respect your time. We start with an initial consultation to understand your specific business risks and operational needs. Every firm is different; a Wickford-based solicitor has different security priorities than a logistics company in Tilbury. We then conduct both on-site and remote testing using industry-leading diagnostic tools to probe your defences. This isn’t a “one size fits all” exercise. The final result is a comprehensive, easy-to-read report. We prioritise our recommendations so you know exactly which vulnerabilities need immediate attention and which can be managed as part of your long-term roadmap.
Beyond the Audit: Long-Term Security Partnerships
An audit is only useful if you act on the results. We don’t just hand you a report and walk away. We help you turn those findings into a practical action plan. Whether it involves fine-tuning your user permissions or deploying our managed firewalls, we’re here to do the heavy lifting. This seamless integration with our broader IT support packages ensures your security remains a constant priority, not a one-off event. Choosing a local IT support company in Essex makes a significant difference. We understand the regional landscape and provide a level of responsive, personalised care that larger national providers often lack. We’re part of your community, and we’re invested in your success.
Secure Your Business Future with Confidence
Protecting your livelihood in 2026 requires more than just hope. A professional IT security audit Essex is the most effective way to identify hidden vulnerabilities and ensure your firm meets essential UK compliance standards. Whether you need the baseline protection of Cyber Essentials or a deep-dive bespoke assessment, the goal remains the same. You’re building a resilient business that can withstand evolving cyber threats. By organising your assets and preparing your team, you turn security from a source of anxiety into a strategic advantage.
Networking2000 has been the local veteran for Essex businesses since 1998. Based in Wickford, our expert team provides the safe pair of hands you need to navigate complex digital risks. We don’t just find the problems; we provide a comprehensive post-audit roadmap to help you fix them. It’s time to stop guessing about your network safety and start knowing. Book your expert IT security audit with Networking2000 today and let us handle the technical details. We’re ready to help you build a safer, more stable future.
Frequently Asked Questions
How much does an IT security audit cost for an Essex SME?
Costs vary based on your company’s size, the number of devices on your network, and the depth of testing required. A basic assessment for a micro-business is naturally less intensive than a full manual review for a firm with multiple sites. We suggest looking at current industry averages for a professional IT security audit Essex, but the best approach is always a tailored quote that reflects your specific infrastructure and risk profile.
How long does a typical IT security audit take to complete?
Most audits are completed within one to two weeks from the initial consultation to the delivery of the final report. The on-site or remote technical testing usually takes one or two days. The remaining time is spent analysing the data and drafting prioritised recommendations. Larger Essex firms with complex cloud setups or multiple local offices may require a slightly longer timeframe to ensure every endpoint is thoroughly checked.
Will an IT security audit cause downtime for my business?
A professional audit won’t cause downtime or interrupt your daily operations. We use non-intrusive testing methods and schedule intensive scans during your off-peak hours to maintain network performance. Our goal is to observe your systems in their natural state without breaking anything. You can continue serving your clients whilst we work in the background to identify your digital vulnerabilities and strengthen your defences.
What is the difference between a vulnerability scan and a full audit?
A vulnerability scan is an automated tool that searches for known software bugs, whereas a full audit is a comprehensive, human-led evaluation. Scans are excellent for catching missing patches, but they can’t assess whether your staff are sharing passwords or if your remote access policies are weak. A full IT security audit Essex combines these automated tools with expert analysis of your physical security and internal processes.
How often should my business undergo a security audit?
You should aim for a professional security review at least once every twelve months. Annual audits are often a requirement for maintaining Cyber Essentials certification or meeting insurance policy conditions. It’s also vital to trigger a new audit if you undergo significant changes, such as moving to a new office in Wickford, migrating to the cloud, or adopting a permanent hybrid working model for your team.
Do I need an audit if I already have a managed firewall?
Yes, because a managed firewall is a single defensive layer, not a complete security solution. Even the best firewall can’t protect you if a staff member accidentally clicks a phishing link or if your internal user permissions are set too high. An audit verifies that your firewall is configured correctly and identifies gaps in other areas, such as device management and data encryption, that a firewall doesn’t cover.
Can an IT security audit help me with GDPR compliance?
Audits are essential for demonstrating that you’ve taken “technical and organisational measures” to protect personal data as required by UK law. The process identifies where sensitive information is stored and who can access it. This helps you comply with the Data (Use and Access) Act 2025. By fixing the weaknesses found, you significantly reduce the risk of a breach that could lead to heavy ICO fines.
What happens if the audit finds significant weaknesses in my network?
Finding weaknesses is actually a positive outcome because it allows you to fix them before a criminal exploits them. Your audit report will include a prioritised list of findings, categorised by risk level. We focus on the “critical” and “high” risks first to give you immediate protection. From there, we work with you to implement a practical action plan that strengthens your network without disrupting your budget or operations.

