Would you bet your firm’s entire reputation on the hope that your current IT setup isn’t a “leaky bucket”? With 43% of UK businesses reporting a cyber breach in the last year, many local directors realise that a professional business IT security audit Essex specialists provide is the only way to stay ahead. You might feel overwhelmed by the 2026 Danzell updates for Cyber Essentials or fear that a thorough check-up will cause massive disruption to your daily operations.
We believe that security should provide clarity, not complexity. A professional assessment gives you a clear, prioritised roadmap rather than a list of confusing technical problems. This guide explores how an independent audit identifies hidden vulnerabilities and ensures your firm meets the latest UK compliance standards. You’ll discover how to secure your data, satisfy supply chain requirements, and finally gain the peace of mind that your business is protected by a truly resilient infrastructure.
Key Takeaways
- Identify why a comprehensive health check is vital to protect your firm against the automated cyber threats targeting regional businesses in 2026.
- Discover how a professional business IT security audit Essex experts perform uses a “layered defence” framework to pinpoint hidden vulnerabilities.
- Learn why an independent assessment is critical for spotting the technical blind spots and configuration drift that internal teams often overlook.
- Gain a practical roadmap that guides your firm through the entire process, from technical data collection to the final implementation of security fixes.
- Understand the advantage of local expertise and how a seasoned partner helps you maintain compliance with the latest UK security standards.
What is a Business IT Security Audit and Why Does Your Essex Firm Need One in 2026?
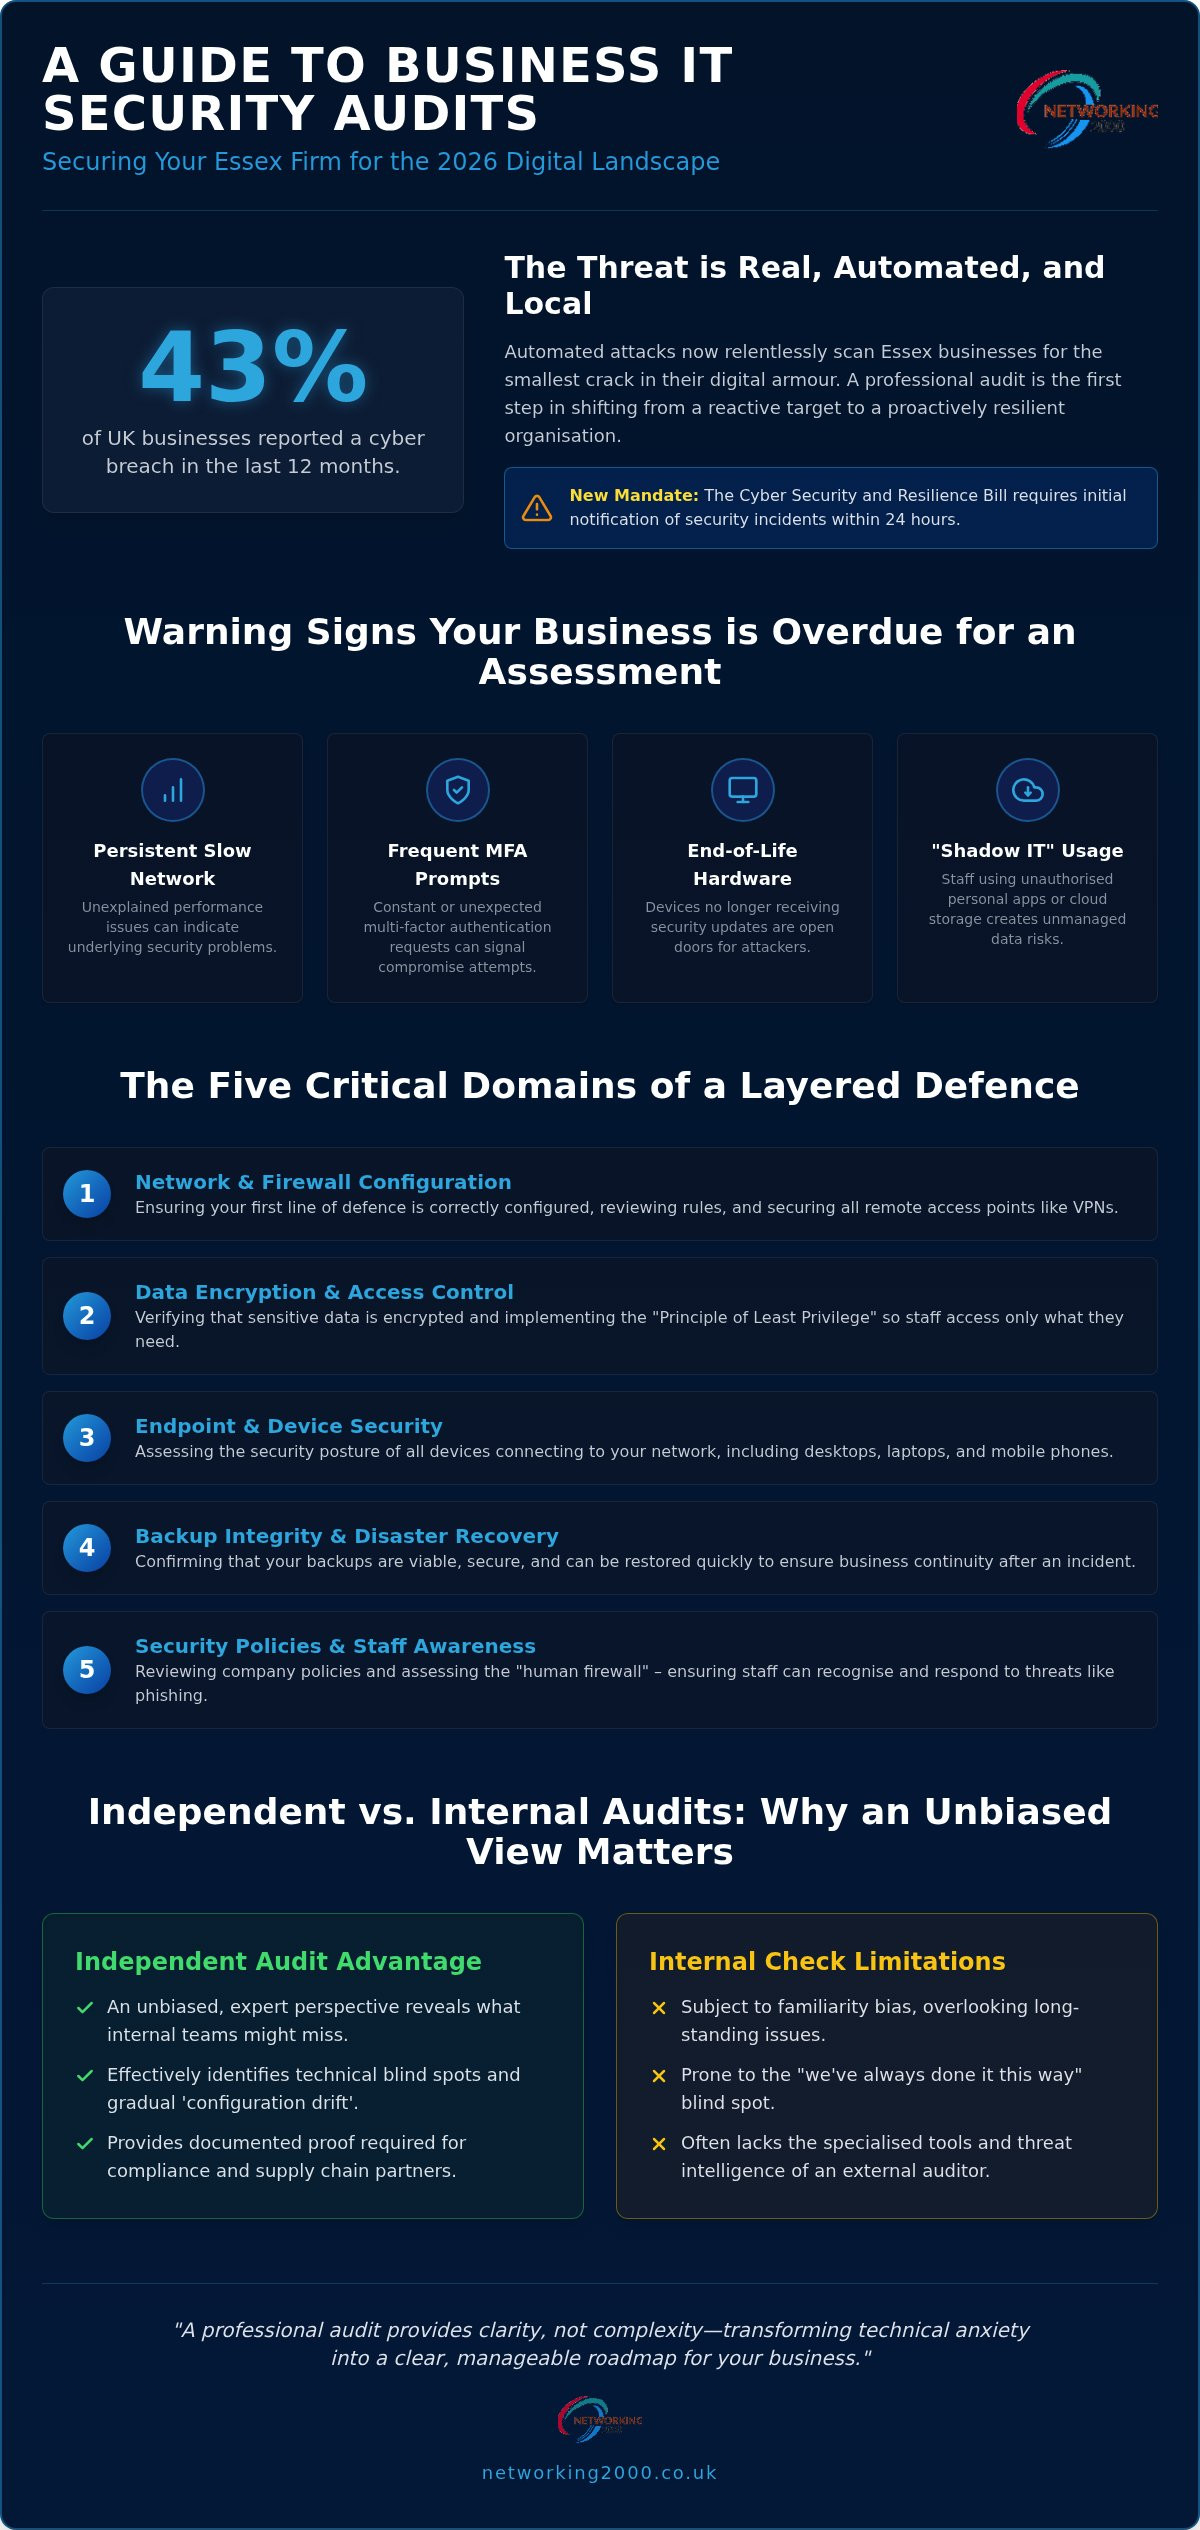
A professional audit is far more than a simple password check. Think of it as a comprehensive health check for your entire digital infrastructure. Whilst a basic security scan might find an obvious patch missing, a full-scale audit examines your people, processes, and hardware. To understand the foundational scope, it is helpful to ask: What is an information security audit? Essentially, it is a deep dive into how your data is handled and protected at every level. In 2026, the threat landscape has shifted significantly. Automated attacks now target Essex businesses regardless of their size, scanning for the smallest crack in your armour.
With 43% of UK businesses reporting a breach in the last 12 months, the risk is no longer theoretical. Shifting from a reactive mindset to proactive resilience is now the core goal for any stable firm. Waiting for a breach to happen before fixing a problem is a strategy that leads to expensive downtime and damaged reputations. A business IT security audit essex experts conduct provides the visibility you need to fix “leaky buckets” before they become disasters. It turns technical anxiety into a clear, manageable roadmap for your business.
The 2026 Compliance Landscape: Cyber Essentials and Beyond
The “Danzell” version of Cyber Essentials introduces stricter requirements for 2026. It makes it impossible for firms to simply “tick boxes” without genuine, documented proof of their security posture. Additionally, the new Cyber Security and Resilience Bill has introduced stringent reporting mandates. Businesses are now required to provide an initial notification of a security incident within 24 hours. If you are part of a local Essex supply chain, your larger partners will now demand a business IT security audit essex report before they consider renewing your contracts or awarding new tenders.
Signs Your Wickford Business is Overdue for an Assessment
Firms relying on legacy systems often harbour hidden vulnerabilities that remain invisible until a malicious actor exploits them. You do not need to be a technical expert to spot the warning signs that your current setup is failing. Look out for these common red flags:
- Persistent slow network performance that cannot be explained by hardware age.
- Staff being bombarded with frequent, unexpected Multi-Factor Authentication (MFA) prompts.
- Using hardware that has reached its “end of life” and no longer receives critical security updates.
Shadow IT is another growing risk for local firms. This happens when staff use unauthorised personal apps or cloud storage because they find your official systems too restrictive. An audit identifies these gaps, allowing us to provide secure, managed alternatives that keep your team productive whilst keeping your data under your control.
The Five Critical Domains of a Professional Security Assessment
A robust business IT security audit essex firms commission relies on the framework of “layered defence”. This approach ensures that if one security measure fails, others remain in place to block the threat. It isn’t just about software. A professional assessment covers physical hardware and infrastructure too. By following professional security assessment guidelines, we examine every digital entry point to your business. Since 1998, Networking2000 has specialised in these core infrastructure areas, offering a “safe pair of hands” for local enterprises seeking to harden their defences.
Network Integrity and Managed Firewall Configuration
Your firewall is your first line of defence. An audit reviews your current rules to ensure they still align with your specific business needs. We check for open ports that shouldn’t be there and verify that remote access points, such as VPNs, are secure. Configuration drift happens over time; what was secure six months ago might be a vulnerability now. If your configuration is outdated, you might benefit from managed firewall Essex services to maintain constant, professional protection.
Data Encryption and Access Control Protocols
We evaluate how sensitive client data is stored and who has the right to see it. A key part of this assessment is the “Principle of Least Privilege”. This ensures staff only have access to the specific files they need for their roles, which limits the damage if an account is compromised. We also review your backup integrity. This step confirms your disaster recovery plan will actually work when you need it most, rather than failing during a crisis.
The Human Element: Social Engineering and Training
Technology is only half the battle. Your employees are often the strongest or weakest link in the chain. An audit assesses staff awareness regarding phishing and “vishing” (voice phishing) threats that bypass technical filters. We review password hygiene and ensure multi-factor authentication (MFA) is correctly implemented across the firm. This holistic view is why many local directors choose Networking2000 to handle both their technical infrastructure and procedural security training.
Independent Auditing vs Internal IT Checks: Why the Distinction Matters
Every business needs an objective perspective to maintain a truly resilient network. When an internal team manages a system daily, they naturally focus on immediate availability and user performance. Security, however, requires a different lens. An independent business IT security audit essex firms invest in serves as a vital benchmark against industry standards. It identifies “configuration drift”—those slow, incremental changes to settings that can create massive gaps over time. Insurance providers and stakeholders also demand neutral third-party reports to verify compliance, as self-assessment often lacks the necessary weight for high-level risk management.
A fresh pair of eyes can spot the subtle errors that become invisible to those who work with the infrastructure every day. It isn’t about finding fault; it’s about ensuring that your digital assets are protected by the most current methodologies. This external validation provides a level of certainty that internal reviews simply cannot match, especially when navigating the complex regulatory changes expected throughout 2026.
The Limitations of In-House Security Reviews
Most in-house IT professionals are stretched thin. Between resolving user tickets and maintaining server uptime, there is rarely enough time for the forensic level of detail a professional audit requires. There is also the inherent risk of confirmation bias. When you have built and maintained a system yourself, it’s difficult to see your own errors or outdated habits. You might assume a protocol is still effective because “it’s always worked that way,” whilst an auditor knows that specific protocol is now a known vulnerability. You can read more about balancing these roles in our guide on managed IT support vs in-house IT.
How Networking2000 Partners with Your Existing Team
We don’t view our role as a replacement for your trusted staff. Instead, we act as a supporting partner and a “safe pair of hands.” A business IT security audit essex specialist can actually help internal managers by providing the hard data needed to secure more budget for necessary upgrades. We translate complex technical findings into a clear, prioritised “to-do” list. This allows your team to focus on implementation whilst we provide the independent validation that your board of directors requires. It’s about creating a collaborative environment where technical expertise and objective auditing work together to protect the firm.
Your 2026 Security Roadmap: From Initial Audit to Implementation
A business IT security audit essex specialists perform is more than a list of technical faults. It is a strategic journey designed to move your firm from uncertainty to resilience. The process begins with scoping. We tailor the assessment to your specific sector and business size, whether you are a small practice in Wickford or a larger firm in Chelmsford. Next, we move to technical data collection. This phase uses advanced vulnerability scanning to find cracks in your digital perimeter that automated attacks might exploit. We then review your internal policies and user behaviour patterns to see how data actually moves through your office. Finally, we present our findings in a jargon-free report and implement a roadmap to achieve managed IT support services excellence.
Interpreting Your Audit Report Without the Jargon
We believe that security reports should be readable. We categorise every identified risk into four clear levels: Critical, High, Medium, and Low. This allows you to see exactly where your budget will have the most impact. We focus heavily on “Quick Wins” during the early stages of implementation. These are straightforward fixes, such as updating firewall rules or closing unused ports, that provide immediate protection. Our reports avoid long, winding narratives. We use short, punchy sentences to explain technical flaws to directors. This ensures everyone in the boardroom understands the risks and the solutions without needing a background in computer science.
Achieving Cyber Essentials Certification in Essex
A professional audit acts as an essential “pre-test” for government-backed certifications. The 2026 Danzell updates for Cyber Essentials have introduced stricter requirements, particularly regarding mobile device management (MDM) and cloud security. These updates ensure that even when staff work remotely, your corporate data remains under your control. Securing this certification is a strategic advantage for local firms. It is often a mandatory requirement for winning larger Essex County Council contracts or securing a place in corporate supply chains. By identifying gaps early, we help you meet these 2026 standards with confidence. If you are ready to start your journey toward a more secure infrastructure, contact our team to book your initial security review today.
Securing Your Wickford Business with Networking2000
Choosing a partner to handle your digital safety is a significant decision for any director. Since 1998, Networking2000 has acted as a “safe pair of hands” for SMEs across Essex and London. Our heritage is built on providing reliable, proactive support that allows you to focus on your core operations. We don’t believe in flashy marketing speak or overcomplicating technical issues. Instead, we offer straightforward, honest advice that addresses your specific risks without the unnecessary fluff often found in the industry. Being based in Wickford gives us a distinct advantage. We understand the local business landscape and can provide a faster, more contextual response than national competitors who might not even know where your office is located.
A business IT security audit essex firms receive from us is grounded in this practical approach. We look at your infrastructure through the lens of a long-term partner, not just a one-off consultant. This local insight helps us understand the specific supply chain pressures and regulatory requirements facing firms in our region. If you are currently evaluating your options, our guide on choosing the best IT support companies in Essex provides a neutral framework to help you make the right choice for your firm’s future.
Tailored Security Solutions for Essex SMEs
We do not believe in “one size fits all” security bundles. Every business has a different risk profile, and your audit should reflect that. We scale our assessments to fit your exact needs, whether you are a growing team of 10 or an established firm with 150+ users. Our primary goal is to keep your business running whilst we secure it. We organise our technical scans and policy reviews to ensure minimal disruption to your daily workflow. This methodical approach ensures that your “leaky bucket” is repaired without causing a flood of downtime for your staff.
Next Steps: Book Your 2026 Security Assessment
Your journey toward a more resilient infrastructure starts with a simple discovery call. During this initial conversation with our Wickford team, we will discuss your current setup, your growth plans, and any specific compliance worries you have regarding the 2026 updates. We’ll explain our process clearly so you know exactly what to expect. With the next wave of UK compliance deadlines approaching, now is the best time to organise your business IT security audit essex. Proactive planning is always more cost-effective than reactive fixing after a breach has occurred. Contact Networking2000 today to secure your digital future and gain the peace of mind that comes from professional, local expertise.
Future-Proof Your Essex Firm with Professional Security
Maintaining a resilient digital infrastructure is no longer an optional extra; it’s the foundation of your firm’s stability. By identifying hidden vulnerabilities and aligning with the 2026 Danzell updates, you protect both your reputation and your place in the local supply chain. A professional business IT security audit essex ensures you aren’t just ticking boxes, but building a genuine layered defence against automated threats.
Since 1998, Networking2000 has been the “safe pair of hands” for regional businesses. As Cyber Essentials specialists, we provide independent, jargon-free reporting that turns complex technical data into a prioritised roadmap for your team. You don’t have to navigate the evolving threat landscape alone. Our Wickford based experts are ready to help you move from reactive fixing to proactive resilience.
Take the first step toward total peace of mind. Book Your Comprehensive 2026 IT Security Audit Today and ensure your business is ready for whatever the next year brings.
Frequently Asked Questions
How long does a business IT security audit Essex typically take?
A standard business IT security audit Essex firms require usually takes between one and three days for the technical assessment phase. The exact duration depends on the complexity of your network and the number of users in your organisation. Once the data collection is complete, we provide a detailed report within a week. This timeline ensures we capture a thorough snapshot of your vulnerabilities without causing prolonged disruption to your operations.
Will an IT security audit cause downtime for my staff in Wickford?
No, a professional audit is designed to be non-intrusive and should not cause downtime for your staff. We use passive scanning techniques and review configurations in the background. Our Wickford based team organises the assessment to work around your daily schedule, ensuring your productivity remains high whilst we identify security gaps. We prioritise keeping your business running smoothly throughout the entire technical review process.
What is the difference between a vulnerability scan and a security audit?
A vulnerability scan is an automated tool that searches for known software bugs and missing patches. In contrast, a full security audit is a comprehensive, human-led evaluation of your entire digital environment. This includes reviewing internal policies, user behaviour patterns, and physical hardware security. Whilst a scan identifies technical flaws, an audit provides the strategic context needed to build a truly resilient infrastructure for your firm.
How much does a professional IT security audit cost for a small business?
The cost of a professional assessment depends on several factors, including the number of users, the complexity of your infrastructure, and the specific compliance standards you need to meet. Every business has a unique risk profile, so we tailor the scope to suit your requirements. We focus on providing a clear return on investment by identifying critical risks that could lead to far more expensive data breaches or operational downtime.
Do I need a security audit if I already have an antivirus and firewall?
Yes, because antivirus software and firewalls are only individual layers of a much larger defence system. An audit checks if these tools are correctly configured and identifies gaps they might miss, such as poor password hygiene or insecure remote access points. Even the best software cannot prevent human error or “shadow IT” usage. A regular check-up ensures your technical tools are working in harmony with your business policies.
Can a security audit help my Essex business with GDPR compliance?
Yes, a security audit is a vital tool for maintaining GDPR compliance. It helps you map where sensitive client data is stored and who has access to it, which is essential for meeting UK data protection standards. By identifying vulnerabilities in how you handle personal information, the audit provides the documented proof of due diligence that regulators require. This proactive approach helps your Essex business avoid the heavy fines associated with data mismanagement.
What happens if the audit uncovers major security flaws in our system?
If we identify major flaws, we immediately categorise them by risk level and provide a prioritised roadmap for remediation. Our goal is to fix “critical” vulnerabilities first to provide immediate protection. We work as a “safe pair of hands” to help your team implement these fixes without causing operational chaos. Discovering a flaw during an audit is always better than finding it after a malicious actor has exploited it.
How often should my business schedule a full security assessment?
We recommend scheduling a full assessment at least once every twelve months. However, you should also consider a new audit if you undergo significant changes, such as moving to a new office, migrating to the cloud, or hiring a large number of staff. With the 2026 Danzell updates to Cyber Essentials, regular checks ensure you remain compliant with the latest UK standards whilst protecting your firm from evolving automated threats.

